Hi everyone. In today’s article, we’ll introduce the browser session management option available in Microsoft Entra Conditional Access policy. We’ll create a session control policy for administrator access to applications hosted in Azure. This policy, combined with second-factor control, ensures that whenever an administrator opens a new browser, they must authenticate using MFA.
Conditional Access persistent browser session (preview)
The persistent browser session allows the user to remain signed in to an application even after closing and reopening the browser. It presents the user with the “Stay signed in?” option after authenticating to Azure using a browser.
We’ll carry out the following activities throughout this article:
1 – Creating the Conditional Access policy requiring users with Global administrator privileges to present a second authentication factor for access to all applications in Azure.
2 – Access tests without session control enabled.
3 – Configuring session control in the Conditional Access policy.
4 – Access tests with session control enabled.
Creating the Conditional Access policy with MFA
We’ll create the Conditional Access policy by accessing the Conditional Access policies menu through this link.
Select the New policy option.
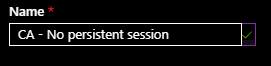
Enter the policy name in the Name field.
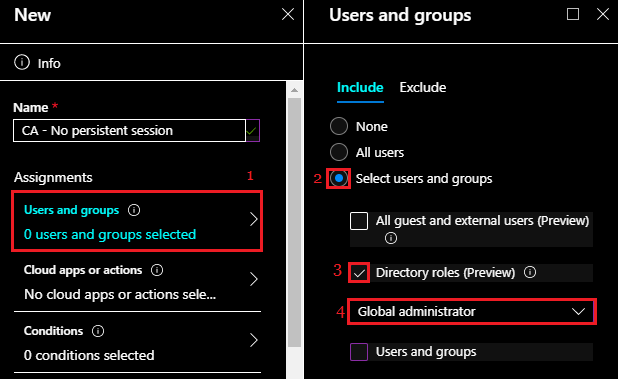
We’ll select the Global administrator role to be assigned to this policy by performing the steps below:
1 – Select the Users ans groups option.
2 – Select the Select users and groups option.
3 – Check the Directory roles (Preview) option.
4 – Select the Global administrator role from the list.
Click Done.
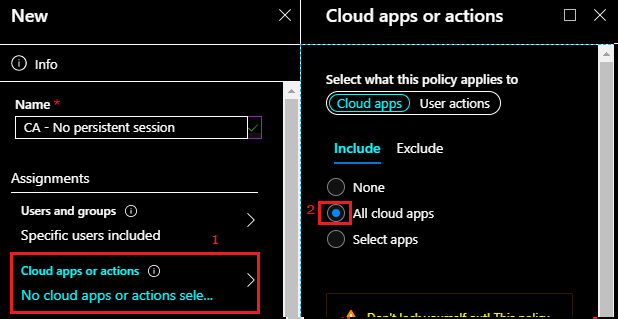
We’ll select all Azure applications by performing the following steps:
1 – Select the Clouds apps or actions menu.
2 – Select All cloud apps.
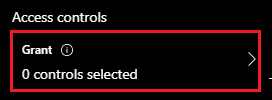
We’ll set the requirement to perform second-factor authentication by selecting the Grant option in the Access controls menu.
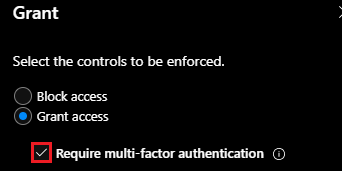
Check the Require multi-factor authentication option.
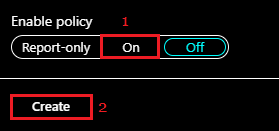
We’ll enable the Conditional Access policy by performing the steps below:
1 – In the Enable policy option, select On.
2 – Click Create.
First access to the Azure portal without session control
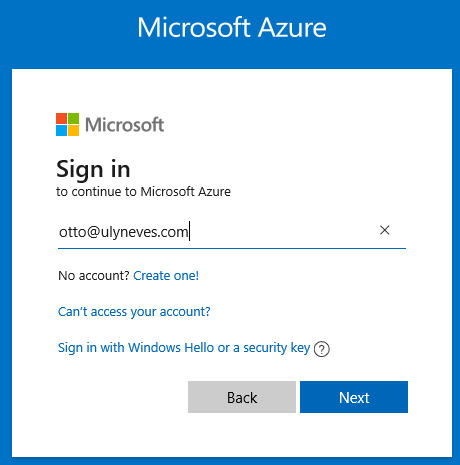
We’ll access the Azure portal at https://portal.azure.com using a credential with Global administrator privileges.
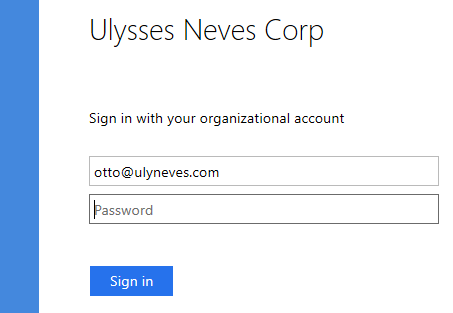
Access is redirected to the AD FS portal to enter the password.
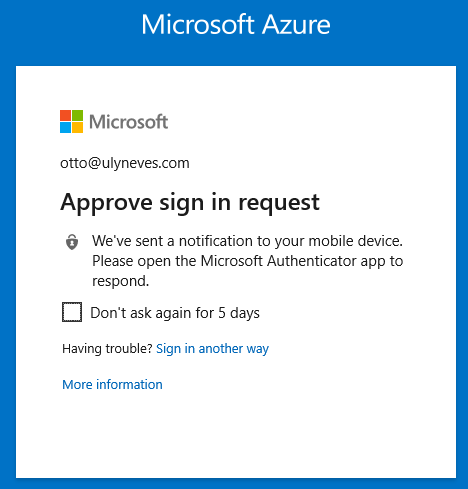
MFA is requested, in this case, through an approval notification to the Microsoft authenticator app.
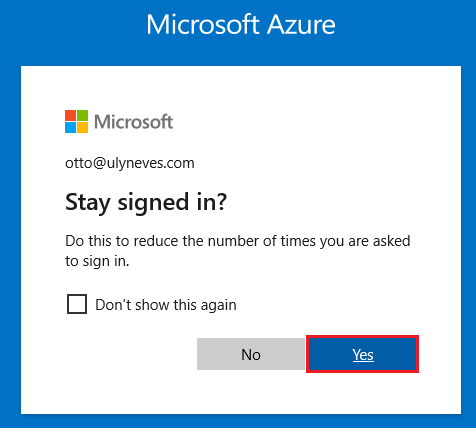
With the MFA step completed successfully, the “Stay signed in?” confirmation is requested, which uses cookies to store the user’s access information and avoid new credential prompts. For more information about this feature, check out this link.
Let’s click Yes.
We can see that access was granted to the Azure portal.
Let’s validate the user experience when accessing the Azure portal for the second time with the access information stored in the cookie.
Second access with keep me signed in
With the access information in the cookies, when accessing the URL https://portal.azure.com, access to the portal is immediately granted without the need to present credentials or a second authentication factor.
We’ll now disable “keep me signed in” through session control in the Conditional Access policy. This setting forces the user affected by the policy to present credentials and the second authentication factor every time they access an application in Azure.
Enabling session control in the Conditional Access policy
We’ll access the “CA – No session persisten session” policy created at the beginning of this article.
In the Access controls menu, select the Session option.
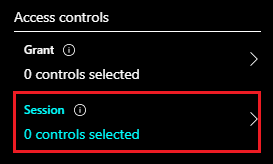
We’ll disable persistent browser sessions by performing the following steps:
1 – Check the Persistent browser session option.
2 – Select the Never persistent option.
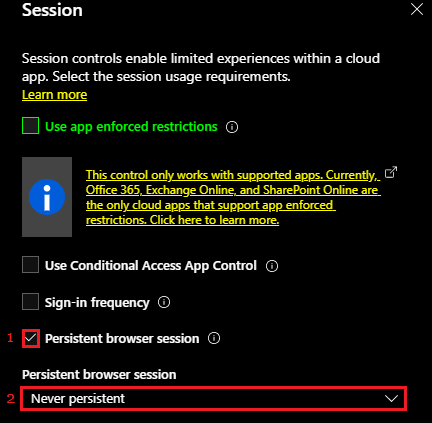
Note: Session control requires that all cloud applications be selected in the Cloud Apps or actions menu.
Click Select and then Save.
Let’s now perform the same Azure portal access test, this time with session control enabled.
First access to the Azure portal with session control
Let’s access the Azure portal again at https://portal.azure.com using a credential with Global administrator privileges.
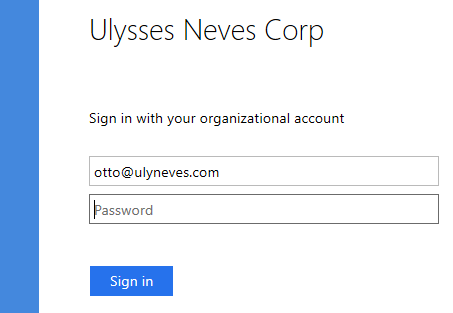
Access is redirected to the Ad FS portal for the user to enter the password.
MFA is requested again through an approval notification to the Microsoft authenticator app.
This time, the “keep me signed in” option is not presented to the user and access is granted to the Azure portal.
Let’s now perform the second access to the Azure portal.
Second access to the Azure portal without keep me signed in
When accessing the URL https://portal.azure.com, the last credential that accessed this application is displayed.
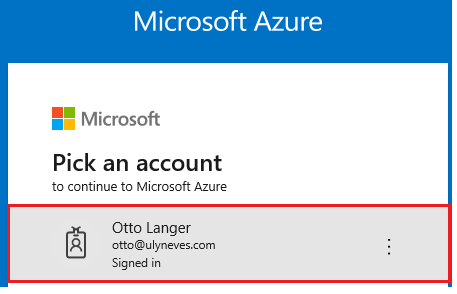
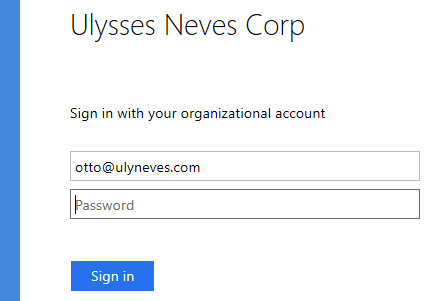
When clicking the credential, the user is redirected to the AD FS portal to enter the password.
MFA is requested as if it were the first access to the portal.
With MFA validation completed, access is granted to the user in the Azure portal.
Summary
In today’s article, we explained what the Persistent browser session (Preview) option available in Microsoft Entra Conditional Access policies is and what it’s used for. We demonstrated the difference in an administrator’s access experience to the Azure portal with persistent session control disabled and enabled using a Conditional Access policy. For more information about this feature, check out this link.
I hope this content has helped enrich your knowledge of Microsoft Entra ID.
Did you like the post? Like and share it. 🙂
If you have any suggestions or comments, let us know.
[ ]’s
Ulysses Neves