Skip to content

Ulysses Neves

Microsoft Entra ID, authentication, and hybrid identity troubleshooting.

Menu
  • Home
  • Microsoft Azure
  • Microsoft AD FS
  • Microsoft 365
  • Contact
  • Troubleshooting Index
Menu

WHfB Cloud Kerberos Trust – Fixing config issue: ‘Cloud trust for on-premise auth policy is enabled: No’

Posted on June 19, 2023

Hello everyone. In this article, I will cover one common issue when moving from WHfB Certificate trust to WHfB Cloud Kerberos Trust. If you are planning to migrate from WHfB Certificate trust to WHfB Cloud Kerberos trust, most probably, you are following this document: https://learn.microsoft.com/en-us/windows/security/identity-protection/hello-for-business/hello-hybrid-cloud-kerberos-trust-provision?tabs=intune#migrate-from-certificate-trust-deployment-model-to-cloud-kerberos-trust

Scenario: WHfB Hybrid Cert Trust to Cloud Kerberos Trust migration
Device join type: Hybrid Azure Ad Joined

In case the deployment is being done via GPO, the settings below should be enabled to cover the computer objects:
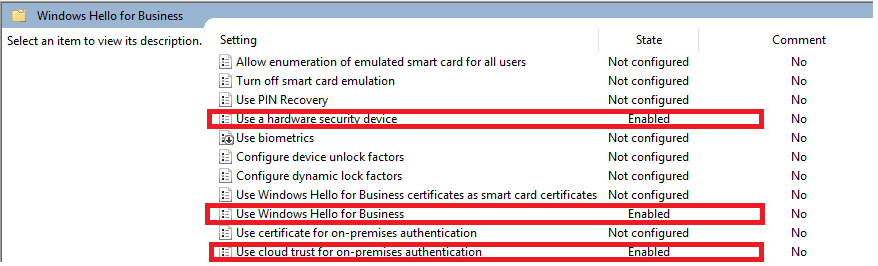
Reference: https://learn.microsoft.com/en-us/windows/security/identity-protection/hello-for-business/hello-hybrid-cloud-kerberos-trust-provision?tabs=gpo#create-the-windows-hello-for-business-group-policy-object

With the policy above configured, looking into the Microsoft-Windows-User Device Registration/Admin event viewer logs and filtering by event ID 358, we find out that the setting Cloud trust for on premise auth policy is enabled is set to No, which means that no WHfB Cloud Kerberos trust will be provisioned.

Windows Hello for Business provisioning will be launched.
Device is AAD joined ( AADJ or DJ++ ): Yes
User has logged on with AAD credentials: Yes
Windows Hello for Business policy is enabled: Yes
Windows Hello for Business post-logon provisioning is enabled: Yes
Local computer meets Windows hello for business hardware requirements: Yes
User is not connected to the machine via Remote Desktop: Yes
User certificate for on premise auth policy is enabled: Yes
Machine is governed by enrollment authority policy.
Cloud trust for on premise auth policy is enabled: No
User account has Cloud TGT: Not Tested
See https://go.microsoft.com/fwlink/?linkid=832647 for more details.

Checking the Microsoft-Windows-User Device Registration/Debug event viewer logs and filtering by event IDs 500 and 503, we find detailed steps during Ngc policy check:

NgcPolicy::IsDeviceStateReadyCore started
NgcPolicyCheck: FailFast is set to TRUE
NgcPolicyCheck: { NgcPolicy::VerifySessionIsNotRemote } stage succeeded
NgcPolicyCheck: { NgcPolicy::GetUserAccountType } User type is DJ++ and user has a PRT ( domain join + AAD Join )
NgcPolicyCheck: { NgcPolicy::VerifyPrimaryAccountHasPrt } stage succeeded
NgcPolicyCheck: { NgcPolicy::VerifyDeviceIsJoined } stage succeeded { device is joined }
NgcPolicyCheck: { NgcPolicy::GetNgcPolicyState } Platform policy returned by NgcQueryEnabled. NgcEnabledState = 1 (NgcEnabled), NgcPolicySource = group policy, NgcPolicyModifiers = certificate is required for on-prem auth, ProvisioningSuccessExpected = TRUE
NgcPolicyCheck: { NgcPolicy::VerifyNgcIsEnabled } stage succeeded { NGC policy is NgcEnabled }
NgcPolicy::VerifyAccountHasCloudTgt – hr: 0x00000000. UseCloudTrustForOnPremAuth = No, CertificateRequiredForOnPremise = Yes, AccountHasCloudTgt = Not Tested, CloudTgtPresent = FALSE.
NgcPolicyCheck: { NgcPolicy::VerifyMachineMeetsNgcRequirements } stage succeeded { provisioning is expected to succeed on this machine }

With the events above, we can see that Certificate Trust configuration is still enabled. As per event ID 6441 in the Microsoft-Windows-HelloForBusiness/Operational logs result, we confirm that Windows Hello for Business certificate trust and cloud trust policies are both enabled. Certificate trust policy will be enforced.

Troubleshooting:

Running RSOP command on cmd, we find the conflicting policies configured below:
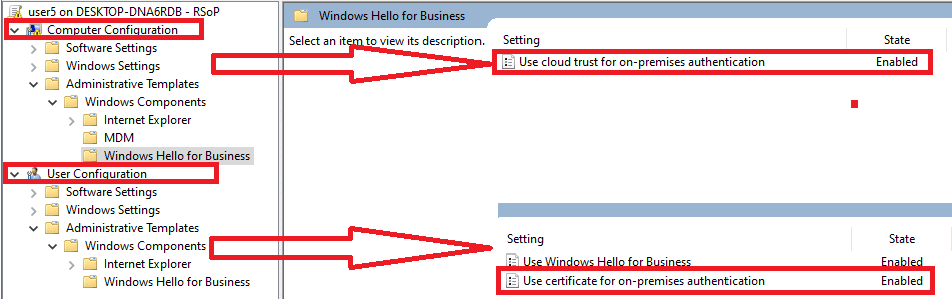
If the Use certificate for on-premises authentication policy is enabled, certificate trust will take precedence over cloud Kerberos trust. Ensure that the machines that you want to enable cloud Kerberos trust have this policy not configured or disabled.

Reference: https://learn.microsoft.com/en-us/windows/security/identity-protection/hello-for-business/hello-hybrid-cloud-kerberos-trust?tabs=gpo#configure-windows-hello-for-business-policy

FIX: To fix this issue, we should disable the User’s GPO with ‘User certificate for on-premises authentication’ setting enabled. Once the GPO changes apply to the user/machine, during the next logon, the user should be prompted for the WHfB Cloud Kerberos Trust.

Summary

In this article, we covered how to identify and fix the GPO conflict that causes the status ‘Cloud trust for on premise auth policy is enabled: No’.

I hope you have enjoyed reading this article, and it helps you manage your WHfB Cloud Kerberos trust deployments.

Enjoyed the article? Like and share. 🙂

Note: I do not represent the organization I work for, all the opinions expressed here, are my own. This post is provided AS IS with no warranties or guarantees and confers no rights.

In case you have any suggestions or feedback, please leave a comment.

[ ]’s
Ulysses Neves

Related guides: Browse the Microsoft Identity Troubleshooting Index or the Windows Hello for Business topic archive.

Leave a Reply Cancel reply

Your email address will not be published. Required fields are marked *

Recent Posts

  • Microsoft Defender for Identity domain investigation: six questions to ask first September 10, 2026
  • Microsoft Entra Kerberos key rotation: what changes—and what administrators should check September 6, 2026
  • Microsoft Authenticator Will Block Jailbroken Devices in 2026 — What You Need to Know March 17, 2026
  • Enhancing Azure role activation security with FIDO2/Passkeys September 23, 2024
  • Microsoft Entra ID CAP | Enforcing WHfB using Authentication Strength April 21, 2024

Archives

  • September 2026
  • March 2026
  • September 2024
  • April 2024
  • February 2024
  • December 2023
  • September 2023
  • July 2023
  • June 2023
  • May 2023
  • April 2023
  • March 2023
  • February 2023
  • January 2023
  • December 2022
  • October 2022
  • September 2022
  • August 2022
  • July 2022
  • June 2022
  • May 2022
  • April 2022
  • March 2022
  • February 2022
  • January 2022
  • December 2021
  • November 2021
  • October 2021
  • September 2021
  • August 2021
  • July 2021
  • June 2021
  • May 2021
  • April 2021
  • March 2021
  • February 2021
  • January 2021
  • December 2020
  • November 2020
  • October 2020
  • September 2020
  • August 2020
  • July 2020
  • June 2020
  • May 2020
  • April 2020
  • March 2020
  • February 2020
  • January 2020
  • December 2019
  • November 2019
  • October 2019
  • September 2019
  • August 2019
  • July 2019

Tags

#aaddownleveldevice #adfs #adfscertificate #adfscertificates #adfsmfaadapter #azureauth #azureCA #azuredevice #capolicy #cloudsummit2021 #conditionalaccess #conditionalaccesspolicy #deviceregistration #farmbehavior #gopasswordless #mfaserver #msidentity #namedlocation #securingazure #securingazuread #sslprivatekey #troubleshootingadfs #troubleshootingwaptrust #tshootadfs #waptrust #webapplicationproxy #WHFBcerttrust #whfbdeployment #WHfBhybridsetup #WHfBprovisioning #widdatabase adconnect AD FS authenticationstrength az500 azurepim Azure security cloudsecurity microsoft365 Microsoft Azure Microsoft Entra hybrid join Microsoft Entra ID Microsoft Entra MFA PowerShell WHfB
©2026 Ulysses Neves | Design: Newspaperly WordPress Theme
Ulysses Neves
Gerenciar Consentimento de Cookies
Para fornecer as melhores experiências, usamos tecnologias como cookies para armazenar e/ou acessar informações do dispositivo. O consentimento para essas tecnologias nos permitirá processar dados como comportamento de navegação ou IDs exclusivos neste site. Não consentir ou retirar o consentimento pode afetar negativamente certos recursos e funções.
Funcional Always active
O armazenamento ou acesso técnico é estritamente necessário para a finalidade legítima de permitir a utilização de um serviço específico explicitamente solicitado pelo assinante ou utilizador, ou com a finalidade exclusiva de efetuar a transmissão de uma comunicação através de uma rede de comunicações eletrónicas.
Preferências
O armazenamento ou acesso técnico é necessário para o propósito legítimo de armazenar preferências que não são solicitadas pelo assinante ou usuário.
Estatísticas
O armazenamento ou acesso técnico que é usado exclusivamente para fins estatísticos. O armazenamento técnico ou acesso que é usado exclusivamente para fins estatísticos anônimos. Sem uma intimação, conformidade voluntária por parte de seu provedor de serviços de Internet ou registros adicionais de terceiros, as informações armazenadas ou recuperadas apenas para esse fim geralmente não podem ser usadas para identificá-lo.
Marketing
O armazenamento ou acesso técnico é necessário para criar perfis de usuário para enviar publicidade ou para rastrear o usuário em um site ou em vários sites para fins de marketing semelhantes.
  • Manage options
  • Manage services
  • Manage {vendor_count} vendors
  • Read more about these purposes
Ver preferências
  • {title}
  • {title}
  • {title}