Encountering error code ‘0x000005e’ during PIN-based authentication in Windows Hello for Business (WHfB) can be a roadblock for users. In this blog post, we’ll delve into a specific scenario where users face this issue immediately after the enrollment process in a cloud Kerberos trust scenario.
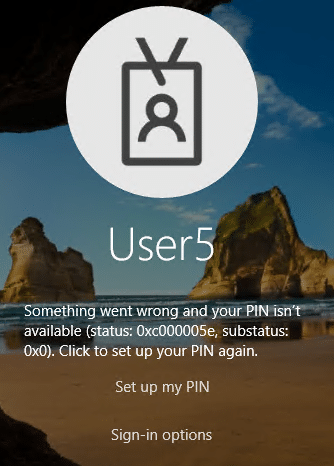
Issue: Users attempting to use WHfB might be greeted with error code ‘0x000005e,’ signaling a hurdle in the authentication process. The error message, often cryptic, can leave users scratching their heads.
Investigation: Upon checking the logs, specifically event ID 302 in Microsoft-Windows-Kerberos/Operational, a common culprit emerges. The error message points to a Kerberos client facing communication issues against two domain controllers:
Events 302: The Kerberos client was bound to domain controller DC1.corp.contoso.com for the domain CORP.CONTOSO.COM but could not access this domain controller at the time.
DesiredFlags: 16777216
CacheFlags: 0
ErrorCode: 0xC000005E

The Kerberos client was bound to domain controller DC2.corp.contoso.com for the domain CORP.CONTOSO.COM but could not access this domain controller at the time.

    DesiredFlags: 16777217
    CacheFlags: 0
    ErrorCode: 0xC000005E
Reason: In order to simulate the lacking line of sight with a domain controller, I blocked connections to my domain controllers using outbound rules in the client’s firewall. In a real scenario, network communication is required to exchange the partial TGT to get a full TGT as explained in the Microsoft public doc: https://learn.microsoft.com/en-us/windows/security/identity-protection/hello-for-business/hello-how-it-works-authentication#microsoft-entra-hybrid-join-authentication-using-cloud-kerberos-trust
Solution: Make sure the device has line of sight with a domain controller when attempting to use the PIN for the first time.
Sign-in
Once a user has set up a PIN with Cloud Kerberos trust, it can be used immediately for sign-in. On a Microsoft Entra hybrid joined device, the first use of the PIN requires line of sight to a DC. Once the user has signed in or unlocked with the DC, cached sign-in can be used for subsequent unlocks without line of sight or network connectivity.
Reference: https://learn.microsoft.com/en-us/windows/security/identity-protection/hello-for-business/deploy/hybrid-cloud-kerberos-trust-enroll?tabs=intune#sign-in
Conclusion:
Wrapping up, we explored strategies for investigating and resolving the ‘0x000005e’ error encountered in Windows Hello for Business Hybrid Cloud Kerberos trust deployment. I trust that this article has not only been informative but will also empower you in effectively managing your Windows Hello for Business environment.
Did you find this article helpful? Consider showing your appreciation by liking and sharing it. 🙂
Disclaimer: The views expressed in this post are personal and do not represent the opinions of my organization. The provided solution is offered “AS IS” without warranties or guarantees and should be validated in a test environment before deployment in production.
Your suggestions and feedback are invaluable; feel free to leave a comment.
[ ]’s Ulysses Neves
